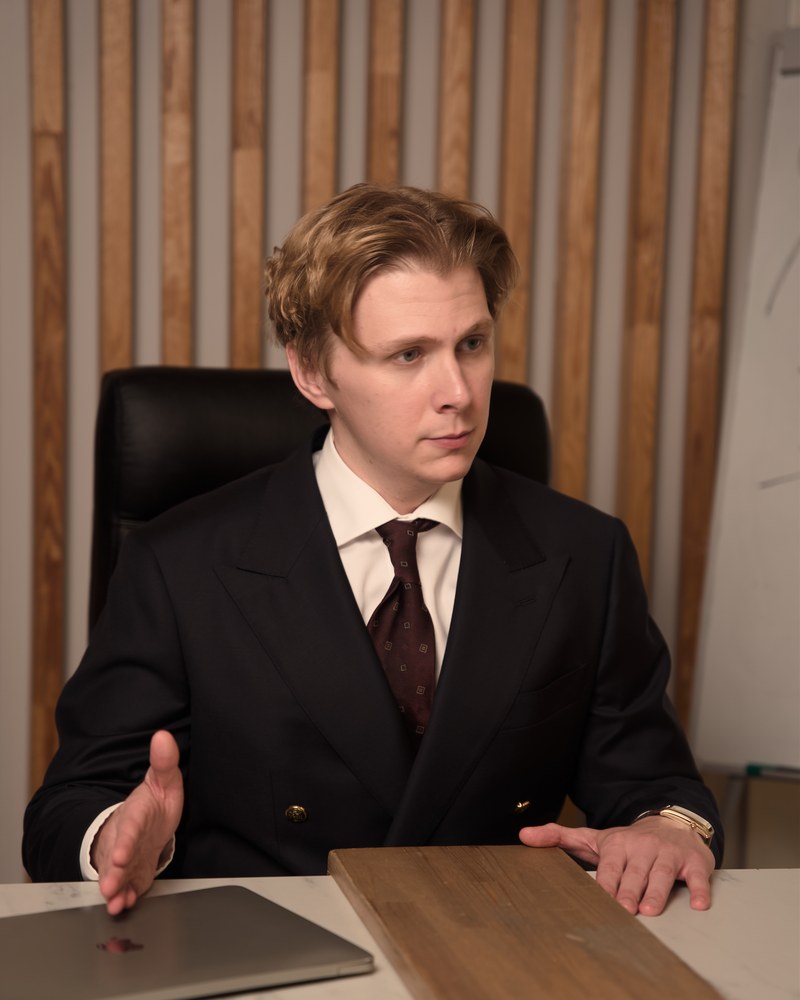
Independent expert in information security and critical information infrastructure (CII) protection.
My focus is the regulatory gap: the backbone infrastructure of the financial sector, meaning clouds, DNS and hosting, remains outside the regulatory perimeter for significant CII objects. I file comments on draft acts by FSTEC, the FSB, the Ministry of Digital Development, the Bank of Russia and sector ministries and agencies, including the Ministries of Transport, Finance, Labour, Health, Emergencies and Science and Higher Education and the Federal Medical and Biological Agency. I sent proposals on the anti-fraud package to the State Duma Committee on Information Policy, Information Technology and Communications and work with the Digital Economy Development Council at the Federation Council. Master's student at RANEPA, programme in Public Administration and National Security.
Focus areas and approach to work, in Russian. The player opens on click: until then the page does not contact the video platform. The same clip on RUTUBE and VK Video.
Areas of work
CII regulation
Comments and proposals on draft acts published for public consultation: from the anti-fraud package and its secondary regulation to information infrastructure security indicators, requirements for artificial intelligence in state systems and the status of fintech infrastructure, meaning digital assets and crypto exchanges, outside the perimeter of Federal Law 187-FZ.
Parliamentary track
The State Duma Committee on Information Policy, Information Technology and Communications, the Digital Economy Development Council at the Federation Council, and the ROCIT commission on cloud technologies, hosting and information security.
Research
Master's thesis at RANEPA: protecting the national payment system infrastructure from cyberattacks.
Results
March to September 2026. Every item is backed by a document or a consultation page.
Proposals on the regulation on the federal state information system "Centralised System for Collecting Information of System-112", EMERCOM of Russia
On the draft government decree (ID 01/01/08-26/00170371) the developer marked 9 proposals out of 16 as accepted and another 6 as partly accepted, each with a revised clause: a 10 working day deadline for access instead of 30 with a reasoned refusal, notification of security breaches within 24 hours, restore checks from backups at least once a quarter, and preservation of the information owner's rights when operator functions are transferred.
Developer summary of proposals of 22.09.2026. The act is not yet adopted, this concerns the revised draft.
Six proposals included in the revised text of a draft government decree
On the draft amendments to Government Decree No. 861 of 24.10.2011 (ID 01/01/08-26/00170295, the unified system for the provision of state and municipal services and the state services portal) the developer included six proposals out of seven: handling of downtime of the unified system with that period excluded from deadlines, a hard deadline for erasure or anonymisation of received data, publication of the connection manual with deferred application of format changes, limits on third-party access, minimum privileges for the operator in the role model, and a six-month transition period for accession agreements.
Developer letter of 04.09.2026 with the revised text and the summary of proposals. The act is not yet adopted, this concerns the draft text.
Proposals on 210-FZ secondary regulation accepted by the Digital Ministry
On the draft rules for telecom operator reimbursement (ID 00169315) the ministry accepted suspension of deadlines while the state information system for countering offences committed with the use of information and communication technologies is unavailable and the forwarding deadline, and increased the reconciliation interval from 4 to 6 hours (24 was proposed). On the phone number criteria (ID 00169312) the status is "partly accepted": the number clearing mechanism on the state services portal was confirmed.
Developer comments on the consultation pages, recorded 30.07.2026.
Proposals on the anti-fraud package reviewed by the State Duma Committee on Information Policy, Information Technology and Communications
Expert proposals on draft law No. 1110676-8 were reviewed by the committee, with two official responses signed by chairman S. Boyarsky. The law was adopted as Federal Law No. 210-FZ of 26.06.2026.
Committee responses No. 3.27-24/118 of 27.03.2026 and No. 3.27-24/1283 of 24.06.2026.
Proposals on the calculation of information infrastructure security indicators, FSTEC of Russia
On the draft government decree "On the procedure for calculating the quantitative values of indicators characterising the security level of information infrastructure objects of bodies (organisations)" (ID 01/01/04-26/00167663) two proposals out of four were marked accepted in the summary: independent sample verification of the calculation, and inclusion of financial organisations. The revised text has not been published.
FSTEC official summary of proposals.
Policy briefs to the Digital Economy Development Council at the Federation Council
A brief on the infosec workforce gap following the meeting of the section on technological sovereignty and information security of the Russian Federation, and a brief on classifying digital currency infrastructure as CII, passed to the office of A. Sheikin, deputy chairman of the Council.
Briefs of 19.05.2026 and 01.06.2026.
Filings where proposals were not accepted
On the amendments to Order No. 677 on information protection in hosting of state systems (168142) the official summary of 25.06.2026 shows that of the 10 proposals from participants 0 were accepted, 1 partly accepted and 9 rejected, mine among them. On the cryptographic protection requirements for state systems (169883) the summary of 01.09.2026 rejected all three proposals. A formal inquiry to the Information Security Department of the Bank of Russia on the gap between NKTsKI and FinCERT notifications received a signed response noting the proposals. On the drafts on DNS resolution and the national domain name system (167678) and on cloud infrastructure for state systems (167984) no outcome has been published.
Consultation summaries, Bank of Russia response to inquiry ref. OE-220338.
XIII Snesarev Readings, RANEPA
Talk "Analysis of technical gaps in fintech cybersecurity regulation": the regulatory gap thesis presented to the academic community.
XIII Snesarev Readings programme.
Primary sources: the draft law No. 1110676-8 record on sozd.duma.gov.ru and the public consultation summaries on regulation.gov.ru.
In 2026 I filed comments on 59 draft acts and standards. The outcome is known for 31 of them: what was accepted and what was not.
Expertise
Nine years in IT infrastructure, including inside the CII perimeter of the financial sector: regulatory proposals built on engineering experience, not theory.
Municipality 2.0
July to September 2026, completed. Led the IT track of a municipal governance digitalisation project: built and launched a team performance bot for the district.
National Settlement Depository
3.5 years in engineering roles at systemically important financial market infrastructure, with ownership of technical decisions: technical policy for server infrastructure import substitution.
Ministry of Health federal contract
Contributor to the "Digital Twin of Healthcare Processes" federal project: infrastructure in air-gapped environments.
RANEPA
Master's programme in Public Administration and National Security, thesis on protecting the national payment system infrastructure.
Publications and talks
Next appearance
14 October 2026, "Intelligent Enterprise 2026" forum by Open Systems publishing house, Moscow: interactive session "Who is responsible for an AI agent? Law, risks and economic security". 12 November 2026, CNews Forum 2026, Moscow.
Telegram channel "Na stadii obsuzhdeniya": breakdowns of draft CII and information security regulations while they can still be changed, and what was accepted. Mirrored on MAX: "Na stadii obsuzhdeniya", in Russian.
Profiles and affiliations
- Expert of the NTI Platform registry, public profile, since 24 August 2026.
- Lecturer of the Russian Znanie Society, since 1 September 2026.
- ORCID: 0009-0006-8187-4528.
- Author pages: BIS Journal, D-Russia.ru.
- Video introduction: RUTUBE, VK Video.
How I can help
Alongside my public work on draft regulations, I take on a limited number of engagements from companies. The format is advisory: analysis, briefs, training. I do not perform work requiring FSTEC licences, such as attestation or technical protection of information.
Breaking down 210-FZ requirements for a bank or telecom operator
The main provisions of 210-FZ take effect on 1 March 2027 and some on 1 September 2027; the draft secondary regulation is also set for 1 March 2027: integration with the state information system for countering offences committed with the use of information and communication technologies, reimbursement of stolen funds, and data exchange with telecom operators. I will give your team a clear picture: which processes to build, the deadlines and risks, and what to watch in the final wording of the decrees. I filed proposals on these drafts and the Digital Ministry marked some of them as accepted, so I know the documents first-hand.
Methodological support for CII object categorisation
187-FZ and Government Decree No. 127: I help you work out which of your systems fall under categorisation, how to prepare the object inventory and justify the categories. I act as a second pair of eyes for your categorisation commission: methodological support, review of contested points, checking documents before submission.
Requirements for artificial intelligence in protected systems
FSTEC is preparing amendments on artificial intelligence to the requirements under Order No. 117, and a draft national standard on secure development of AI software is under discussion in parallel. I will explain what applies to your systems and what to ask a model vendor now: the requirements, the timeline, and the questions for the contract and the architecture. I filed comments on both documents and wrote analyses of them for industry media.
A seminar on CII and infosec regulation for your team
A live walkthrough of current requirements for IT and infosec specialists, lawyers and compliance: what is already in force, what takes effect within the year, what is still under discussion and where a position can still be filed. Based on my own filing practice and correspondence with regulators. One and a half to two hours, online or in person in Moscow.
If this sounds like your situation, write to my e-mail with a short description. The initial conversation is free and carries no obligation, and we discuss the fee once the scope is clear.
For editors and organisers
I comment on CII regulation, the secondary regulation under 210-FZ, FSTEC requirements, artificial intelligence in protected systems and the protection of financial sector infrastructure. Requests are best sent by e-mail, I reply the same or the next working day.
How to introduce me
Nikolay Lobanov, independent expert in information security and critical information infrastructure protection, master's student at RANEPA
Short bio
Independent expert in information security and critical information infrastructure protection. Files comments on draft acts by FSTEC, the FSB, the Digital Ministry, the Bank of Russia and other agencies, with some proposals marked accepted by the developers.
Full bio
Independent expert in information security and critical information infrastructure protection. Nine years in IT infrastructure, including systemically important financial market infrastructure. Since 2026 takes part in public consultations on draft regulations, with some proposals on the anti-fraud secondary regulation and on information infrastructure security indicators marked accepted by the developers. Author of articles in BIS Journal, D-Russia.ru, Bankovskoe Obozrenie, CIO Russia, PLUSworld, Cyber Media, BISA and CISOCLUB. Master's student at RANEPA, programme in Public Administration and National Security.
Photographs
Press kit: full size photographs, bios and comment topics on a separate page. If you need a different shot, write to my e-mail.
Contact
Press comment on CII regulation, participation in public consultations on draft acts, review of regulatory documents, business enquiries from companies.
E-mail: nlobanov-25 [at] ranepa.ru
Press, regulators, event organisers and business enquiries
Telegram: @na_stadii
Draft regulation breakdowns, in Russian
MAX: max.ru/channel_na_stadii
Mirror of the Telegram channel